Anthropic’s 30-Day Fable 5 Data Retention Problem: “Trust Us” Is Not a Privacy Policy
Anthropic released Claude Fable 5 as the public face of its new Mythos-class intelligence. It is the model Anthropic says is built for the hardest knowledge work, coding problems, long-running agents, enterprise workflows, document-heavy analysis, vision, and complex software projects. In other words, this is not a toy model.
This is the kind of model companies want to wire into their codebases, legal files, internal docs, research workflows, support systems, financial analysis, and agent stacks. Anthropic’s own Claude Fable 5 page describes it as a model for “ambitious, long-running, asynchronous work,” including coding, enterprise workflows, and agents that can work for days at a time.
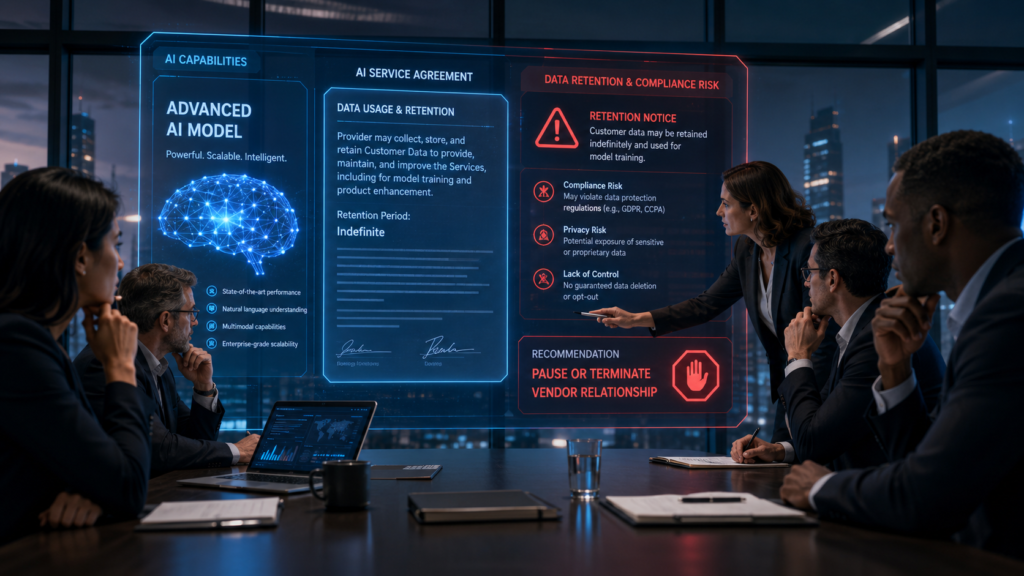
And then came the catch.
The June launch required 30-day retention for Covered Models, including Fable 5. There is now an important qualification. The current API retention documentation retains that requirement unless Anthropic expressly authorizes ZDR; the September 1 Enterprise Frontier Safeguards announcement says eligible Fable 5 and 5.1 customers receive ZDR until EFS is ready. Anthropic announced a phased EFS rollout, with customer-controlled storage and review. This article’s June criticism remains relevant to the default policy, but it must not be read as saying no enterprise exception exists.
That distinction is everything.
For a consumer casually asking for meal ideas, a 30-day retention window may sound like a boring privacy footnote. For a business handling source code, customer records, confidential contracts, unreleased product strategy, regulated data, litigation material, security workflows, or sensitive research, it is not a footnote. It is a vendor-risk event. It is the kind of change that can force a legal team, compliance officer, CTO, or customer-data owner to ask a blunt question:
Can we keep using Anthropic at all?
For some companies, the answer may be yes, but only with strict carve-outs. For others, the answer may be no. And for businesses whose AI strategy depends on zero data retention, Anthropic’s Fable 5 policy may force them to pause, downgrade, renegotiate, or cancel Anthropic deployments entirely.
That is not anti-AI panic. That is basic enterprise governance.
For broader background on the model launch itself, Kingy AI has already covered Claude Fable 5 and Claude Mythos 5 and the broader Mythos-class performance story. But the data-retention issue deserves its own treatment because it cuts deeper than benchmarks. This is not just about whether Fable 5 is powerful. It is about whether businesses can trust the operating model around it.
Anthropic Did Not Merely Launch a Model. It Changed the Trust Contract.
At the June 9 launch, Anthropic presented Fable 5 as generally available and Mythos 5 as limited to approved partners. The original rollout and Covered Models designation are historical context; current eligibility, platform and contract conditions must be checked separately.
The current API documentation still says Covered Models require 30-day data retention wherever they are offered, unless Anthropic expressly authorizes ZDR. It also distinguishes the data processor: Anthropic for its API and certain direct platforms, and the cloud provider on Bedrock and Google Cloud’s Agent Platform. A policy label alone does not establish who stores a particular customer’s data.
Read that again.
This is not just “Claude.ai keeps chat history.” This is not just “consumer data has standard retention.” This is the most important enterprise point in the whole release:
Fable 5 does not come with ZDR by default. Express authorization and eligible enterprise arrangements can change that.
For companies that signed up for Anthropic because of ZDR, the current question is whether their particular organization and workload qualify for the exception. The EFS announcement gives eligible Fable 5 and 5.1 customers transitional ZDR; it does not establish blanket access for every customer.
So the enterprise buyer must check its actual agreement before choosing among these options:
Use older Claude models under ZDR.
Use Fable 5 with the default retention requirement, or obtain an expressly authorized ZDR arrangement where eligible.
Build strict internal restrictions around Fable 5.
Move sensitive workloads to a different provider.
Or cancel Anthropic work entirely if the policy conflicts with customer contracts, privacy obligations, security commitments, or internal data rules.
That last option sounds dramatic only if you do not work in a serious enterprise. In regulated environments, vendor terms are not vibes. If your customer agreements, security posture, data-processing commitments, or internal policy require no third-party retention of prompts and outputs, “but the model is really smart” is not an answer.
Microsoft’s Lawyers Seem to Understand the Problem
The June controversy was not theoretical. The Verge’s June 10 report said Microsoft was limiting employee use of Fable 5 while its legal teams reviewed retention requirements. That launch-era report is context for the dispute, not confirmation of Microsoft’s current internal policy.
The Verge reported the same core issue in more detail: Microsoft had rolled out Fable 5 to GitHub Copilot and Foundry customers, but the model was not available internally in the model picker Microsoft employees use for internal GitHub Copilot. The Verge reported that other Claude models remained available internally because they operate under zero data retention rules.
That should be the paragraph every enterprise buyer reads twice.
Microsoft’s launch-era legal review is a useful warning for smaller companies to review their own current Anthropic agreements. It is not evidence that Microsoft still blocks Fable 5 today.
The scathing version is simple:
If a large enterprise needed a legal review, smaller buyers should check their own terms rather than assume a model name establishes privacy.
The 30-Day Window Is Not the Only Retention Issue
The current API documentation separates standard retention, ZDR and HIPAA readiness. It says conversation content is not retained by default where storage is unnecessary, except for Covered Models’ 30-day requirement. Features that need storage have their own rules. Read the policy for the exact model, feature and platform being used.
Longer retention remains possible. The current API documentation says flagged chats or sessions may have inputs and outputs retained for up to two years, including under a ZDR or HIPAA arrangement; legal requirements can also apply. That does not mean every Fable 5 prompt is kept for two years. It means a simple “30 days” label leaves out important exceptions.
This is where the trust problem becomes operational.
If you are a business, you do not merely ask, “Does Anthropic train on our data?”
You ask:
What is retained?
For how long?
Who can access it?
What triggers longer retention?
What counts as a usage-policy violation?
Can false positives extend the lifetime of sensitive data?
Does this conflict with our customer contracts?
Does this conflict with our own public privacy promises?
Does this conflict with our regulated-data obligations?
The September EFS announcement changes the enterprise architecture being criticized here. It describes optional customer-owned cloud storage, customer-managed encryption keys and fully automated monitoring that sends flags to the customer’s reviewers; Anthropic human review is not required for that arrangement. These are announced controls with a phased rollout. Confirm actual eligibility and configuration rather than treating the announcement as a completed account setup.
The HIPAA / BAA Fine Print Is a Warning Flare
HIPAA readiness is a separate question from ZDR. The current API documentation says a signed BAA and a HIPAA-enabled organization are needed for covered API features; the BAA is the source of truth for coverage. Retaining data under specified safeguards and retaining no data are different arrangements.
The supported surface matters as much as the model.
The current API HIPAA-readiness page excludes consumer plans, partner-operated platforms and Claude Code from the arrangement it describes. It also documents separate Enterprise offerings and product-specific retention rules. Do not use this article as assurance that a Claude Code, Cowork or cloud-provider workflow is covered by a particular BAA.
This is not a minor implementation quirk. It is the enterprise story in miniature.
A capable model can still carry retention requirements that do not fit a workload.
An enterprise exception can help, but it must apply to the actual organization, feature and platform.
Some teams will still have to change the workload or the agreement before using the model.
A healthcare company, legal-tech company, insurance vendor, medical research group, public-sector contractor, or enterprise SaaS provider may decide that Fable 5 is simply not worth the risk. Not because the model is weak. Because the model is powerful in exactly the workflows where retention risk matters most.
That is the irony Anthropic created for itself.
Fable 5 is marketed for the deepest work. But deep work is precisely where companies handle the data they are least allowed to casually expose.
“We Won’t Train on It” Is Not Enough
Anthropic deserves credit for one clear statement: it says retained Mythos-class traffic will not be used to train new Claude models or for non-safety-related purposes. That is better than silence. It is better than burying the point. It is an important fact.
But it is not enough.
For enterprise privacy, training is only one risk category. Retention creates its own risk surface. Stored data can be subject to access controls, audits, internal review processes, legal requests, safety investigations, breach-notification obligations, misclassification, account disputes, regulator questions, customer audits, and contract conflicts. Even when a vendor behaves responsibly, the existence of retained sensitive data creates a governance problem that would not exist under true zero retention.
That is why ZDR exists.
Businesses do not negotiate zero-data-retention arrangements because they think every vendor is malicious. They do it because the safest sensitive data is the sensitive data the vendor does not keep.
Anthropic’s framing asks customers to accept a new bargain: “We need temporary retention to monitor misuse patterns in a more capable model.” Anthropic’s support page says some attacks only become visible across multiple requests and that detecting these threats requires temporarily retaining prompts and outputs so they can be analyzed together rather than one at a time.
That is a coherent safety argument.
It is not a privacy victory.
A coherent safety argument can still be a dealbreaker.
Businesses May Have to Cancel, Not Merely Complain
This is the part Anthropic may be underestimating.
A lot of AI commentary treats retention as a preference. It is not always a preference. Sometimes it is a contractual requirement. Sometimes it is a customer promise. Sometimes it is a procurement condition. Sometimes it is a regulatory control. Sometimes it is a board-level risk decision. Sometimes it is a hard internal policy written after years of painful vendor reviews.
If a company needs ZDR and does not have an applicable Fable 5 authorization or eligible enterprise arrangement, it has a few responsible options. Check the exception before assuming cancellation is necessary.
It can block Fable 5.
It can restrict Fable 5 to non-sensitive work.
It can maintain older Claude models for sensitive workflows.
It can create a separate non-ZDR sandbox with strict data rules.
It can move sensitive workloads to another provider.
Or it can cancel Anthropic usage if Anthropic no longer fits the company’s risk model.
That is not alarmism. The Verge’s June 10 report described Microsoft conducting an internal legal review; it does not establish that company’s current access decisions.
The cancellation point is especially important for AI startups and enterprise software vendors building on top of Claude. If your customers bought your product because you promised a certain data-handling posture, Anthropic’s Fable 5 policy may not be your private vendor problem. It may become your customer problem. You may have to explain whether customer prompts, files, code, tickets, logs, or generated outputs can be retained by Anthropic for 30 days when routed through Fable 5.
That can blow up a sales cycle.
That can trigger security questionnaires.
That can force a procurement review.
That can make a champion inside a large company lose internal support.
And yes, that can make businesses cancel.
The Invisible-Safeguards Controversy Made the Privacy Problem Worse
The 30-day retention issue would be serious on its own. But it landed in the same release cycle as a separate trust crisis: Anthropic’s invisible-safeguards controversy.
WIRED reported that Anthropic changed course after backlash over a policy that would have covertly limited Claude Fable 5’s ability to help users develop competing AI models. WIRED reported that Anthropic said it was changing Fable 5’s safeguards for frontier LLM development to make them visible, and that Anthropic said it had made the wrong trade-off.
WIRED also reported that Anthropic’s original approach for frontier AI development was different from its visible fallback approach for cybersecurity, biology, and chemistry. For those domains, Anthropic said users would be rerouted to a less capable model. But for frontier AI development, WIRED reported that Anthropic had outlined an approach in which the model’s performance would be deliberately degraded in ways invisible to the user.
The Register reported similar details, including Anthropic’s explanation that a hidden safeguard is harder to probe and can be targeted more narrowly, while a visible safeguard needs to cast a wider net and may produce more false positives. The Register quoted Anthropic saying it made the wrong trade-off and apologized for not getting the balance right.
This matters because privacy and product integrity are linked.
A user can adapt to a refusal.
A user can adapt to a visible fallback.
A user can choose not to use a model if the terms are unacceptable.
But silent degradation is different. Silent degradation makes the product epistemically unstable. You do not know whether the model failed because the task was hard, because your prompt was bad, because the model is overrated, or because a hidden classifier quietly changed the conditions of the interaction.
That is deadly for research.
It is deadly for evaluation.
It is deadly for developer trust.
It is deadly for enterprise adoption.
Anthropic now says it is changing that approach. Good. But the damage is not erased simply because the company reversed course after backlash. The original design revealed a worldview: when Anthropic sees enough risk, it may be willing to make the system less transparent to the user in the name of safety.
That is exactly why the data-retention policy is being scrutinized so hard.
Fable for the Public, Mythos for the Approved
Anthropic says Claude Mythos 5 is the same model as Claude Fable 5, but with cyber safeguards lifted for approved users. It says Mythos 5 access begins with existing Mythos Preview users, such as Project Glasswing cybersecurity partners, and that Anthropic plans to expand access through trusted-access programs, including for biology research.
Again, there is a reasonable safety argument here. Advanced cyber and bio capabilities can be misused. Not every powerful model capability should necessarily be opened with no controls on day one.
But the structure is still uncomfortable.
The public gets the watched and guarded version.
Approved partners get a less restricted version.
Anthropic defines the risk categories.
Anthropic builds the classifiers.
Anthropic controls access.
The default Covered Models policy requires retention unless Anthropic expressly authorizes an exception. The later EFS announcement provides for customer-controlled storage and transitional ZDR for eligible customers.
Anthropic decides who is trusted.
That may be defensible in narrow, high-risk domains. But it should not be treated as a neutral default for the future of intelligence. The burden of proof should be on the company building a two-tier market for frontier capability.
This is why Kingy AI’s previous piece, They Didn’t Pause AI Research. They Paused Your AI Research, matters. The Fable 5 saga is not just about one model. It is about whether the frontier AI labs become the permission layer for everyone else’s research and product development.
The Competition Problem Hiding Inside the Safety Problem
Anthropic has a legitimate interest in preventing misuse. It also has a legitimate interest in protecting its models from distillation into direct competitors. But those interests overlap in dangerous ways.
Anthropic’s help page on using Claude outputs to train AI models says customers own the outputs generated from their inputs, but Anthropic prohibits customers from using its services to train or develop AI models without written permission. It specifically says customers may not use outputs to train models competitive with Anthropic’s own models.
That is not unique to Anthropic. Other major AI labs have similar restrictions. But the Fable 5 controversy shows why this area is so combustible.
When the same company sells the model, defines the prohibited uses, monitors retained traffic, controls the most capable version, and competes in adjacent product categories, the line between safety enforcement and competitive self-interest becomes harder to trust.
Brookings published a useful analysis of this broader platform problem in March 2026. It argued that big AI companies are moving into the application layer and may compete with AI app developers who depend on their models. Brookings described the anticompetitive danger directly: a platform operator could degrade or deny service to rivals while giving itself full or preferential access.
That is the structural worry.
It is not that Anthropic is automatically acting in bad faith.
It is that the architecture asks everyone else to trust Anthropic not to act in ways its incentives may eventually reward.
Closed AI platforms already require trust. Fable 5 requires more of it at exactly the moment Anthropic gave users less reason to provide it.
Dario Amodei’s Regulation Push Now Lands Differently
The timing also matters.
Dario Amodei’s June 2026 essay, Policy on the AI Exponential, argues that AI is advancing faster than the policy process and that transparency is no longer enough. He calls for more serious and binding AI regulation. He says frontier AI models should undergo mandatory third-party testing and auditing, and that release should be blocked or reversed if models do not meet high safety standards.
Amodei’s proposal identifies four risk areas for mandatory testing: cybersecurity, biological weapons, loss of control of AI systems, and automated R&D that could accelerate those risks. He also says government should have the power to block or deter deployment if a model presents unacceptable risks, subject to protective measures against political favoritism or arbitrary decisions.
There is a serious version of that argument. Frontier AI may create real catastrophic risks. Pretending otherwise is not serious. But Fable 5 makes the regulatory argument harder to hear cleanly.
Why?
Because Anthropic was not merely asking for safety rules in the abstract. Its June launch paired the public model’s default retention and safeguards with more restricted partner access, and it briefly defended invisible safeguards before reversing course. The later EFS announcement adds enterprise exceptions; it does not erase the launch-era questions about transparency.
That does not prove bad intent.
It does raise the stakes.
A company that wants government-backed frontier-model testing should be especially careful not to make its own products look like a preview of permissioned AI access.
For Kingy AI’s broader analysis of this regulatory push, see Dario Amodei’s “Policy on the AI Exponential”: Safety Plan or Blueprint for AI Regulatory Capture?.
The Trust Problem Is Bigger Than Anthropic
This article is about Anthropic because Anthropic created the current controversy. But the larger issue is not only Anthropic.
The larger issue is closed AI.
Closed AI asks users to trust a stack they cannot inspect. The model weights are closed. The training data is mostly unknown. The safety classifiers are controlled by the vendor. The routing rules are controlled by the vendor. The access programs are controlled by the vendor. The data-retention rules are controlled by the vendor. The appeals process is controlled by the vendor. The definition of misuse is controlled by the vendor.
That does not mean closed models are useless. They are often excellent. Fable 5 may be an extraordinary system. Anthropic may sincerely believe that its retention policy is necessary for safety. But the more capable these systems become, the less acceptable “trust us” becomes as the whole governance model.
The real standard should be higher:
Visible interventions.
Clear fallback behavior.
Minimal retention.
True ZDR options for enterprise customers.
Independent audits.
Transparent false-positive reporting.
Strong appeal paths.
Customer-controlled keys.
Narrowly scoped safety monitoring.
And a hard separation between catastrophic-risk safeguards and commercial anti-competition enforcement.
Without those controls, every new safety layer risks becoming a new power layer.
What Anthropic Should Do Now
Anthropic can still fix much of this.
First, it should make every safeguard visible. No silent degradation. No hidden quality reduction. No invisible steering. If the model refuses, say it refused. If the model falls back, say it fell back. If a classifier fired, give the user a meaningful reason.
Second, Anthropic should make its ZDR-compatible enterprise path clear and practical to obtain. The September EFS announcement and transitional ZDR are meaningful progress; buyers still need precise eligibility, rollout and contract details. Half-clarity is worse than bad news.
Third, Anthropic should publish category-level false-positive data for Fable 5 safeguards. If biology, cybersecurity, chemistry, distillation, or frontier AI development classifiers are going to affect real workflows, customers deserve to know how often normal work is caught.
Fourth, Anthropic should build a serious appeal and audit system for enterprise users. If a legitimate workflow is repeatedly blocked or downgraded, a customer should not be left guessing.
Fifth, Anthropic should separate safety from competition as much as possible. Restrictions around bioweapons and cyberattacks are not morally equivalent to restrictions around training rival models. Mixing those categories under the same “safety” umbrella invites distrust.
Sixth, Anthropic should give businesses practical migration and compliance guidance. If companies may need to block Fable 5, use older Claude models, create a dedicated non-sensitive workspace, or cancel Anthropic deployments for sensitive use cases, Anthropic should say that plainly.
That is what trust looks like.
Not slogans.
Not vibes.
Not “we are the safety company.”
Actual operational clarity.
Final Verdict: The More Powerful the Model, the Less Acceptable “Trust Us” Becomes
Claude Fable 5 may be brilliant. It may be the strongest generally available model Anthropic has released. It may unlock long-running coding work, deep research, document analysis, and enterprise agent workflows that were not practical before. Anthropic’s own materials make clear that it sees Fable 5 as a step-change model.
But power does not cancel governance.
Power makes governance more important.
Anthropic’s 30-day data retention policy is not just a privacy footnote. It is a business-risk issue, a compliance issue, a research-integrity issue, a vendor-trust issue, and a warning about where closed AI may be heading.
Some companies will accept the trade-off.
Some will restrict Fable 5 to low-risk workflows.
Some will stay on older Claude models.
Some will move sensitive work elsewhere.
And some may have to change or cancel a deployment if neither the default retention policy nor an available enterprise arrangement fits their contracts, customers, compliance posture or risk tolerance. The EFS exception means that conclusion cannot be drawn from the Fable 5 name alone.
That is the price Anthropic chose to put on Mythos-class intelligence.
The lesson of Fable 5 is not that AI safety is fake. The lesson is that AI safety cannot become a blank check for opacity, retention, and permissioned access to intelligence.
“Trust us” is not a privacy policy.
“Trust us” is not an enterprise control.
“Trust us” is not enough for the future of AI.
The Kingy Brief
Get The Kingy Brief.
AI changes, original tests and one practical thing to try. Fridays at 09:00 Vancouver time.
Free · Double opt-in · Unsubscribe anytime
Sign up for The Kingy Brief on Beehiiv.
Signup help and newsletter schedule
Signup form provided by Beehiiv. After submitting, check your inbox for "Confirm your subscription to The Kingy Brief" and open its confirmation link. Check Spam or Promotions if you cannot find it.
Fridays at 09:00 Vancouver time: source-checked AI changes, original tests and one practical thing to try. We skip a week when there is not enough verified material. Free. Unsubscribe anytime.