Launched as an early-beta agent, SpaceXAI’s Grok Bot signs into work tools, keeps running after you close your laptop and coordinates with other Bots. Its persistent-computer design could make AI far more useful—and turn one mistake into a much bigger incident.
Kingy verdict: WATCH. Grok Bot is one of the clearest attempts yet to turn an AI assistant into a durable colleague rather than a disposable chat. The important idea is not that it can click around websites; several rivals can do that. It is that a user’s Bots share one persistent, logged-in cloud computer. Files remain. Sessions remain. Routines remain. Work can continue while the user is away. If you need the product map before the risk analysis, start with what Grok Bot is, how access works and what it costs.
That persistence is the breakthrough and the risk.
If your account is eligible, TRY Grok Bot on one isolated, reversible, low-stakes workflow. Do not give it broad access to production systems, financial accounts, regulated data or an executive’s primary browser profile. Everyone else should WATCH until buyers can verify the limits, audit evidence and failure-handling details for their deployment. High-risk organizations should SKIP deployment for now.
Evidence note: This is a public-source launch analysis, not a hands-on review. Kingy.ai did not have direct Grok Bot access before publication. Capability, security and performance statements attributed to SpaceXAI or Cursor are vendor claims unless otherwise noted. The launch analysis and competitor comparisons use sources checked through September 5, 2026. The access, listed platforms, usage billing and prices below were rechecked against official Grok Bot and pricing pages on October 12, 2026; this does not establish account access or hands-on testing. The October 11 security correction remains limited to the documented shared-computer boundary, storage and privacy settings, and Auto Review rules. Corporate transaction status is updated below from the SEC and Cursor’s acquisition announcement.
Grok Bot at a glance
| Question | Answer |
|---|---|
| What launched? | An early-beta AI “teammate” that can sign into tools, operate websites and apps, remember workflows and work in the cloud. |
| Who can use it? | See the dated access table below. Confirm your own account eligibility. |
| What does it cost? | See the dated access and pricing section below. Confirm your plan quote and account allowance before purchase. |
| What is technically distinctive? | Every user gets one persistent cloud computer shared by all of that user’s Bots, including files, browser state and logins. Isolation is per user, not per Bot. |
| Does it run with the laptop closed? | SpaceXAI says yes: the work executes on its cloud computer. |
| Is it enterprise-ready? | See the dated access table below. Access permission is not Kingy proof of production suitability; the safety and control questions still require a separate assessment. |
| Kingy verdict | WATCH for most; TRY only with a contained pilot; SKIP sensitive production work for now. |
What SpaceXAI actually launched
The launch post describes Grok Bot as an AI teammate that can take a job end to end: sign into a work tool, use the web or an application, ask for approval when needed and return with finished work. The examples include updating a CRM, handling office operations, paying invoices, reproducing a software bug and handing a proposed fix to an engineer.
Those examples are demonstrations and internal testimonials, not independent proof of reliability. Still, the product shape is clear.
Grok Bot has three layers that ordinary chat assistants often lack:
- A durable identity. A Bot can be given a name and a recurring role rather than being recreated for every prompt.
- A persistent workspace. Its files, browser sessions, installed state and logins survive between jobs.
- A collaboration model. Multiple Bots can message one another, participate in a group chat and pass work across the same machine.
SpaceXAI also says a user can demonstrate a workflow once and save it as a routine. That moves Grok Bot closer to an operating layer for repeatable work: part agent, part cloud desktop, part workflow recorder.
The company’s launch post on X called the product an early beta. That was the launch framing, not a status label re-established by this access update. The original concern remains: a consequential product needs public evidence before it can be treated as dependable infrastructure.
The architecture is the story
Most discussions of AI agents focus on model intelligence. Grok Bot’s bigger decision is architectural.
According to the official FAQ, every user’s Bots share one persistent cloud computer. They share the machine’s files, browser and logins so they can preserve context and hand work to one another. The isolation boundary sits around the user, not each individual Bot.
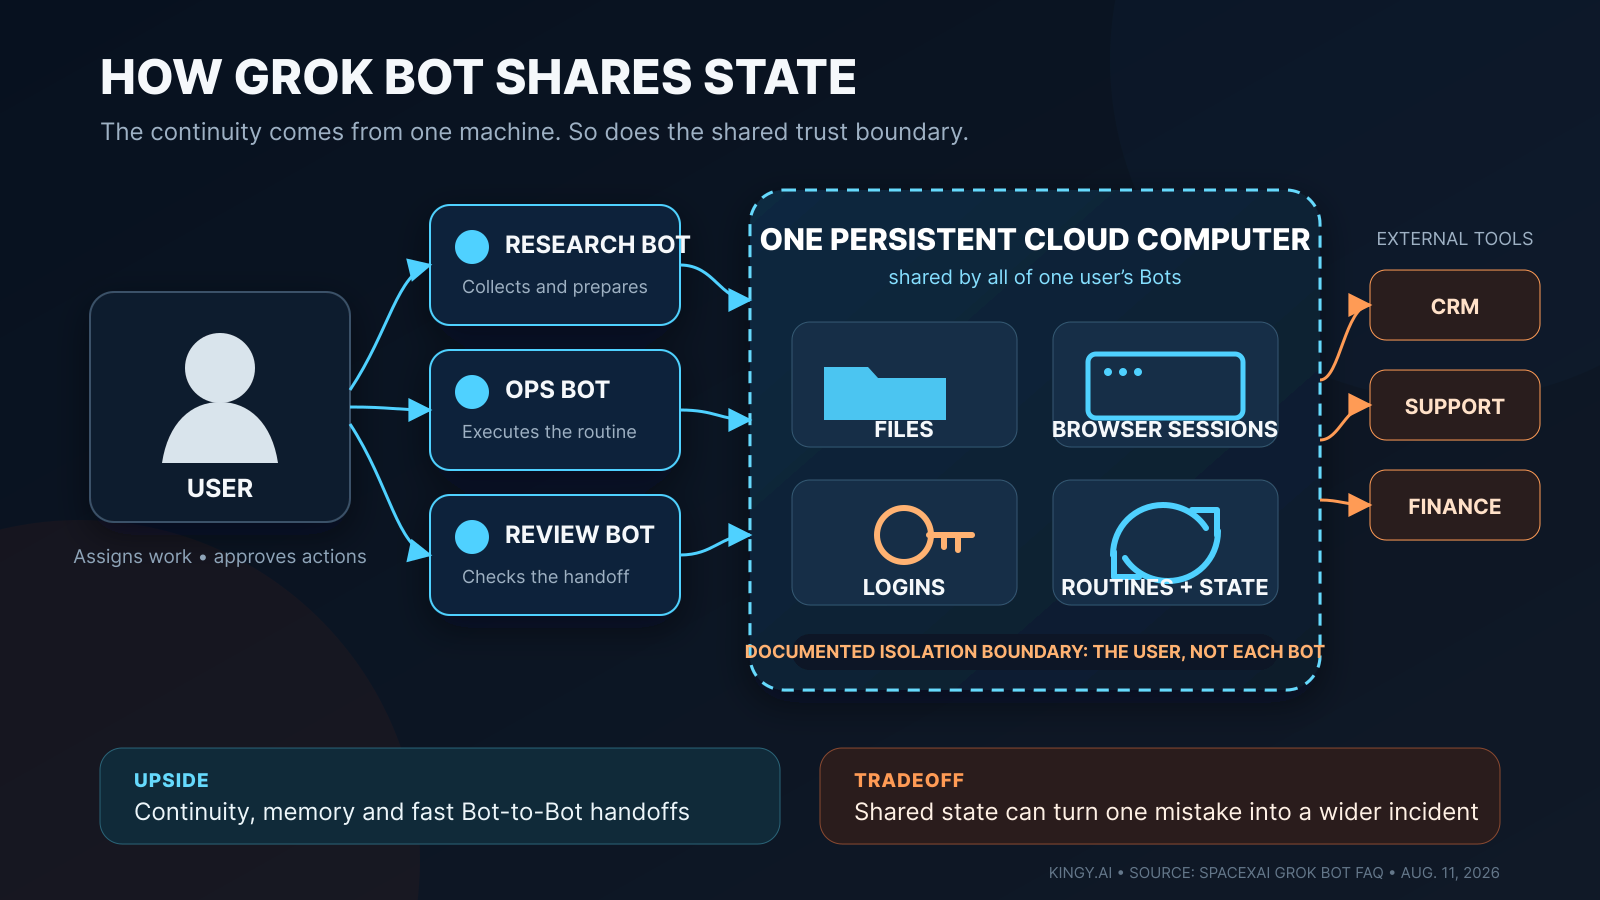
This design has real advantages. A procurement Bot can leave a vendor spreadsheet for a finance Bot. A support Bot can remain signed into a store dashboard. A research Bot does not need to rebuild its environment every morning. The user can close a laptop without terminating the job.
It also creates a larger blast radius.
If one Bot opens a malicious page, mishandles a file or acts on a poisoned instruction, it is operating inside an environment that other Bots use. A browser session established for one role may be available to another. A contaminated file can become shared context. A mistaken configuration can outlive the job that created it.
Named Bots may feel like separate employees. Technically, the public documentation describes them more like separate operators using the same workstation and key ring.
The official Grok Bot security guide, last updated October 6, describes one cloud computer assigned to each user and shared by that user’s Bots, including its files, browser sessions and command-line credentials. It does not specify a Firecracker microVM implementation or say account or plugin access is off by default. Treat the user-level shared computer—not an individual Bot—as the documented isolation boundary.
Access and pricing: simple headline, incomplete economics
Official Grok Bot access and pricing pages checked October 12, 2026 (Pacific): Grok Bot lists Cursor Pro, Pro+ and Ultra; SuperGrok, SuperGrok Plus and Heavy; Cursor Standard and Premium Teams; and Enterprise. The pages list $20/month for Cursor, $30/month for SuperGrok, $100/month for SuperGrok Plus, and $40/seat/month for Cursor Teams. Those are displayed plan prices, not a quote or a per-Bot total; confirm eligibility and billing with the provider. Grok Bot access and plan display; Grok pricing.
| Access route | Grok Bot access | Buyer check |
|---|---|---|
| Cursor Pro, Pro+ and Ultra | Listed by the current FAQ | Confirm account eligibility, weekly allowance and additional-usage settings. |
| SuperGrok, SuperGrok Plus and Heavy | Listed by the current FAQ | Confirm the eligible account and its current plan terms. |
| Cursor Standard and Premium Teams | Listed by the current FAQ | Confirm seat eligibility, usage allowance and the organization’s requirements. |
| Enterprise | Generally available, according to the checked FAQ | Contact sales for setup; separately assess controls and suitability. |
The official Grok Bot page, checked October 12, says subscriptions include weekly Bot usage and additional usage is billed by token cost; its public page does not give the weekly allowance or a complete overage rate card. Check the account’s current limits and billing before use.
A plan price alone does not make operating costs predictable. Agent work can consume far more tokens than a short chat because the system must plan, inspect pages, recover from errors and maintain context across many steps. A useful enterprise evaluation therefore needs cost per completed workflow, not cost per seat or token alone.
The Grok Bot page checked October 12 lists desktop access for macOS or Windows and iOS app access. Linux, Android and minimum OS versions were not confirmed by this answer; omission does not prove non-support. Older X Premium+ and trial routes are likewise unconfirmed, not ruled out.
What looks genuinely useful
The strongest Grok Bot use cases are not open-ended missions. They are bounded jobs that are tedious for a person but easy to inspect after completion.
Examples include:
- collecting CRM notes and drafting follow-ups without sending them;
- reconciling a vendor list and flagging exceptions;
- reproducing a software bug in a disposable environment;
- preparing an invoice packet for human approval;
- monitoring a support queue and drafting responses;
- refreshing a recurring report from approved sources.
Persistence improves these jobs because setup costs disappear. The agent can retain a folder structure, reusable scripts, known sites and the history of earlier runs. Saved routines can reduce repeated prompting. Multi-Bot handoffs can separate research, execution and review—at least conceptually.
But the teammate framing should not obscure a basic reality: an agent that can log in and click is still working through interfaces built for people. A changed button, expired session, CAPTCHA, unexpected modal or ambiguous confirmation page can derail a run. The launch materials do not publish a success rate, a representative task suite, average human-intervention rate or a breakdown of silent versus caught failures.
The available public evidence supports a narrower claim: Grok Bot has the machinery to attempt useful work. The public evidence does not yet establish how often it completes that work correctly.
Security and privacy: the questions buyers should ask first
Launch-period SpaceXAI materials described encryption in transit and at rest, privacy choices and an “Auto Review” layer. The current Grok Bot security guide, last updated October 6, says the product uses Cursor authentication and account data settings, requires data storage, and does not support Legacy Privacy Mode. It says training opt-out follows the applicable Cursor account and privacy settings. The guide directs readers to Cursor’s current security information for infrastructure and encryption details; it does not verify those launch-period claims here. The launch materials also mentioned enterprise DLP policies, certificates, proxies and startup network controls. Their availability still depends on the organization’s rollout and plan.
Those are meaningful claims, but they do not resolve five practical risks.
1. Shared credentials need role boundaries
A persistent login is valuable because the Bot can resume work. It is dangerous because a captured or misused session may remain valuable long after a single task.
The public FAQ says all Bots for a user share logins. It does not explain whether an administrator can prevent a research Bot from using a finance Bot’s session, assign credentials to one Bot only, impose per-site scopes or require fresh approval for privilege escalation. Until that is clear, buyers should assume the user-level computer is the meaningful trust boundary.
2. Prompt injection is an execution risk, not just a bad answer
A webpage, email, document or support ticket can contain instructions designed to redirect an agent. When the agent can only summarize text, the damage may be a corrupted answer. When it can browse authenticated systems, move files and submit forms, the same attack can become an unauthorized action.
Anthropic’s Cowork documentation, checked for this comparison through September 5, explicitly says prompt-injection risk is non-zero. Grok Bot’s public materials cited here do not offer an equivalent threat model or explain how Auto Review distinguishes a legitimate instruction from one embedded in untrusted content.
3. Grok Bot’s current data settings are not a no-storage promise
Cursor’s general data-use disclosure describes how its Privacy Mode and model-provider retention arrangements work, including exceptions. Grok Bot’s current security guide adds a product-specific boundary: Grok Bot requires data storage and does not support Legacy Privacy Mode; privacy and data-sharing choices are managed through Cursor account settings and, when required, the Grok Bot access flow. Do not read the general Cursor disclosure as a promise that Grok Bot avoids storage or has a particular retention period.
The current security guide says training opt-out follows the applicable Cursor account and privacy settings, but it does not give a Grok Bot-specific retention period or map every data flow and model provider. SpaceXAI’s broader consumer privacy policy also says third-party services may be governed by their own policies. Before sharing sensitive data, ask which account settings and contractual terms govern the organization’s deployment.
4. Approvals are only as good as their defaults
The current security guide describes Auto Review rules: “Ask first” takes precedence over “Allow automatically,” administrators can enforce locked team rules, and approval cards show the proposed operation and inputs. It also says Auto Review is model-based and should complement least privilege and explicit boundaries. These documents do not establish complete action coverage, bypass resistance, auditability or rollback; no hands-on test of those behaviors is reported here.
For consequential workflows, approval should attach to the exact action and data—not a vague plan accepted twenty steps earlier.
5. Audit and recovery details are missing
Encryption protects stored and transmitted data. It does not tell an operator what the Bot did, why it did it, which identity it used or how to reverse the result.
The public materials cited in this review do not specify tamper-evident event logs, screen recordings, command histories, administrator exports, retention settings, snapshots, credential revocation behavior or point-in-time rollback. Those omissions are not proof that the capabilities do not exist. They are reasons not to assume they do.
| Risk | Why persistence increases it | Minimum pilot control |
|---|---|---|
| Credential misuse | Sessions survive across tasks and Bots | Dedicated test accounts, scoped roles, no primary admin credentials |
| Prompt injection | Untrusted content can influence an agent with real access | Domain allowlist, read-only access, action-level approval |
| Cross-Bot contamination | Bots share files, browser state and logins | Separate user/computer for each trust zone; sanitize handoff files |
| Silent failure | Long jobs can drift while the user is away | Required evidence bundle, exception alerts, human acceptance check |
| Irreversible action | A completed click may change external state | Draft-only mode, sandbox targets, backups and tested rollback |
| Cost runaway | Multi-step retries consume usage | Spend cap, auto-top-up disabled during pilot, per-workflow accounting |
Reliability and observability: the unglamorous enterprise test
An autonomous system becomes useful when operators can trust both the result and the record.
For every completed job, Grok Bot should ideally return an evidence package: what it changed, what it could not complete, the sources or records it used, the approvals it received and any uncertainty that remains. A status of “done” is not enough for an invoice, a CRM update or a vendor negotiation.
The questions that matter are operational:
- Does a failed job resume safely, or repeat completed actions?
- Can the Bot detect that a page changed halfway through a workflow?
- Are retries idempotent, especially for payments, messages and submissions?
- Can a supervisor see every external action in sequence?
- What happens if two Bots modify the same file or record?
- Can an administrator stop all Bots and invalidate every session immediately?
- Are backups automatic, and how quickly can the computer be restored?
SpaceXAI’s launch pages do not answer these questions. That is normal for a launch announcement. It is not sufficient for production approval.
Grok Bot versus Claude Cowork, ChatGPT Work/Codex and Manus
By the September 5 comparison cutoff, the official sources reviewed described competitors with remote execution, connectors, computer use, scheduled work and durable context in different combinations. This article does not refresh those competitor capabilities in October.
The competitor prices and capabilities in this comparison are historical observations checked through September 5, 2026. The October 12 Grok Bot access and pricing check does not refresh competitor plans or capabilities.
| Product | Durable execution model | Computer/web actions | Price evidence (dates scoped below) | Main distinction |
|---|---|---|---|---|
| Grok Bot | One persistent cloud computer per user, shared by that user’s Bots | Signs into tools and operates apps/web; vendor says work continues with device off | Obtain a current plan quote using the dated access table above. This update does not revalidate the earlier comparison’s price figures. | Named Bots coordinate through one shared, logged-in machine |
| Claude Cowork | Remote sessions, long-running work and scheduled tasks; isolated server-side environment | Browser/computer use plus connectors; local resources require the desktop app connected | Pro $20/mo; Max from $100/mo | Broad knowledge-work surface, remote sessions and explicit permission/admin model; computer use remains a research preview |
| ChatGPT Work + Codex | Long-running work, scheduled tasks and durable agent workflows across ChatGPT/Codex | Connectors and computer-use surfaces vary by product and platform | OpenAI’s pricing page checked October 12 lists Business at $20/user/month billed annually with a 2+ user minimum, or $25/user/month billed monthly. | ChatGPT Work and Codex share plan usage; OpenAI lists ChatGPT and Codex across desktop/mobile, web, CLI and IDE surfaces. This describes its documented surfaces, not a like-for-like shared-computer comparison. |
| Manus Cloud Computer | Dedicated persistent Ubuntu VM that runs continuously outside active sessions | Cloud Browser supports authenticated web actions; the persistent Cloud Computer itself is command-line based | Cloud Computer $10/$30/$50 per month, separate from any applicable agent plan | Most explicit general-purpose persistent server, with direct resource tiers and SSH access |
These are not interchangeable. In this comparison, Claude Cowork and Manus details remain the September 5, 2026 observations above. OpenAI’s October 12 pricing page describes ChatGPT Work and Codex as sharing plan usage and lists ChatGPT/Codex access across desktop and mobile apps, plus Codex on the web, CLI and IDE extension. Those official descriptions do not establish a like-for-like Grok Bot shared-computer model. The competitor comparison has not been comprehensively refreshed.
Grok Bot’s edge is conceptual coherence: create colleagues, give them a computer, let them remember and coordinate. Its weakness is that the same coherence concentrates trust. Competitors that use more isolated sessions or connector-specific permissions may offer less continuity but smaller failure domains.
The strategic angle: Grok is moving beyond the model race
Kingy.ai already tracks Grok as a model and product family and has separately analyzed Grok 4.5’s benchmarks, pricing and context window. Grok Bot is a different contest.
The prize is not the best answer in a benchmark. It is the layer through which work gets assigned, authenticated, executed and remembered.
The launch also arrived during a corporate transition. SpaceX completed its acquisition of xAI on February 2, 2026, according to its SEC filing. SpaceX’s August 14 SEC filing says the Cursor/Anysphere merger became effective that day at an implied $60 billion equity value; Cursor separately announced that it had been acquired by SpaceX. SpaceX SEC filing on its xAI acquisition; SpaceX August 14 SEC filing on Cursor; Cursor’s acquisition announcement.
Grok Bot is distributed through Cursor eligibility and uses Cursor identity and privacy controls, as described in the product materials. That establishes product and account connections; it does not establish a broader integration roadmap or prove that any particular corporate integration is complete.
The strategic logic is strong. Cursor supplies a desktop distribution channel, authenticated users and a culture of agentic work. Grok supplies the model family and consumer brand. A persistent computer expands the combined ambition from writing code to operating a business workflow.
It also raises the cost of weak governance. Grok has faced prior public controversies over harmful generated content, including regulatory scrutiny around sexualized image generation. Those incidents do not establish how Grok Bot behaves. They do mean buyers should ask for evidence rather than treating the teammate label as a trust guarantee. Autonomy magnifies both competence and error.
Legal, ethical and labor questions do not disappear into the cloud
A Bot acting “in your voice” sounds convenient. It can also blur who authorized a statement, whether a recipient knows they are dealing with automation and who is accountable when the Bot overpromises.
Before deployment, an organization should determine:
- whether each target service permits automated browser access under its terms;
- whether employees and customers must be told that an AI agent is acting;
- which records must be retained for negotiations, hiring, finance or regulated decisions;
- who owns the final decision and signs off on representations;
- whether the Bot is allowed to infer preferences from previous work;
- how workers can contest or correct decisions influenced by agent output.
Grok Bot should replace mechanical effort before it replaces accountable judgment. Drafting, gathering and reconciling are sensible early uses. Hiring decisions, disciplinary actions, safety decisions, legal representations and unsupervised financial commitments are not.
“AI teammate” can remove clerical friction or become a surveillance and head-count story. The difference is whether staff shape the workflow, logs are used fairly, humans retain authority and productivity gains improve the job.
How to pilot Grok Bot without betting the company
An eligible team can learn a great deal from a narrow two-week pilot.
- Choose one boring workflow. It should be frequent, reversible and easy to score—such as drafting CRM follow-ups from synthetic records.
- Create isolated accounts. Use a separate test user with the minimum permissions. Do not reuse an executive or administrator browser profile.
- Keep outputs in draft. The Bot may prepare a message, invoice or update, but a human sends or commits it.
- Seed adversarial content. Include a fake instruction in a document or webpage and check whether the Bot follows it.
- Measure completed outcomes. Record success rate, interventions, elapsed time, correction time and total usage cost.
- Test the stop button. Revoke access, invalidate sessions and recover the workspace before trusting the system.
- Review the record. Confirm that the evidence available after a run would satisfy an auditor or incident responder.
Do not expand permissions because a demo looks smooth. Expand only when the measured error rate, controls and recovery process justify it.
Final verdict
Grok Bot is worth watching because its central idea is right: useful agents need continuity. They need a place to work, durable state, recurring routines and a way to hand jobs to one another. A persistent cloud computer provides all four.
But persistence turns yesterday’s convenience into tomorrow’s attack surface. When multiple Bots share files, sessions and logins, the system needs controls that are as durable as its memory. The October 6 security guide now describes account data settings, shared-computer boundaries and Auto Review rules. It does not establish Bot-specific permission isolation, audit trails, task reliability, rollback or incident response, so those controls still need evidence before broad production use.
WATCH if you are evaluating the agent market. TRY it if you already qualify and can isolate a low-stakes workflow. SKIP sensitive or irreversible production use until the system’s controls and operational evidence justify that use.
The real test is not whether Grok Bot can work while you sleep. It is whether, when you wake up, you can prove exactly what it did.
Frequently asked questions
What is Grok Bot?
Grok Bot launched as an early-beta AI agent from SpaceXAI that the company described as a teammate. It can use a persistent cloud computer, sign into tools, operate websites and apps, remember routines and coordinate with other Bots.
Is Grok Bot the same as the Grok chatbot?
No. It belongs to the Grok product family, but Grok Bot is designed for persistent, multi-step work and computer use rather than ordinary question-and-answer chat.
Can Grok Bot keep working when my laptop is closed?
SpaceXAI says yes because work runs on a cloud computer. Teams should verify that vendor claim, continuity and recovery behavior in their own pilot.
Does each Grok Bot get a separate computer?
No. SpaceXAI’s FAQ says every user has one persistent cloud computer and that all of that user’s Bots share its files, browser and logins. Isolation is per user, not per Bot.
How much does Grok Bot cost?
See the dated access and pricing section. Confirm your current quote and allowance rather than relying on the old comparison figures.
Does Grok Bot train on my data?
The current Grok Bot security guide says training opt-out follows the applicable Cursor account and privacy settings. It also says Grok Bot requires data storage and does not support Legacy Privacy Mode. Cursor’s general data-use disclosure describes its own settings and exceptions; organizations should verify which settings, model-provider path, retention terms and policy apply to their Grok Bot deployment before sharing sensitive data.
Is Grok Bot safe for company accounts?
Not by default. The architecture can support useful work, but an agent with persistent authenticated access creates prompt-injection, credential, cross-Bot and irreversible-action risks. Use scoped test accounts, draft-only workflows and action-level human approval.
Is Grok Bot better than Claude Cowork or Manus?
There is no universal winner. Grok Bot emphasizes named teammates sharing a persistent logged-in computer. Claude Cowork offers remote sessions, schedules, connectors and an explicit permission model. Manus offers a dedicated persistent Ubuntu server and a separate authenticated cloud browser. The best option depends on the workflow, control requirements and acceptable failure domain.
Can enterprises buy Grok Bot now?
See Enterprise in the dated access table above. Confirm setup and account eligibility, then separately verify the controls available for your deployment.
Has SpaceX completed its acquisition of Cursor?
Yes. SpaceX’s August 14, 2026 SEC filing says the Cursor/Anysphere merger became effective that day and reports an implied equity value of $60 billion. Cursor also announced the acquisition. These sources confirm the transaction closed; they do not establish a broader product-integration roadmap.
Sources and methodology
This analysis follows Kingy.ai’s source policy, research methodology and editorial standards. Core product evidence includes the Grok Bot launch post, official Grok Bot overview and access page, official pricing page, and security and privacy guide (checked October 11, 2026; overview dated October 7 and guide dated October 6), as well as Cursor’s security and data-use disclosures. Competitor details remain dated to their cited official sources and the September 5, 2026 comparison cutoff. The corporate transaction statements link to the SEC and Cursor sources above.
The October 12, 2026 (Pacific) check updates Grok Bot’s listed access routes, displayed plan prices and weekly-usage billing only. OpenAI Business pricing was checked separately on October 12. Competitor prices and capabilities remain historical through September 5; security statements retain their stated source dates. The corporate transaction status reflects the linked SEC/Cursor sources. None of these checks constitutes a hands-on review or a current checkout/account test.
Disclosure: Kingy.ai did not receive payment, travel, hardware or privileged access for this article. We did not test Grok Bot directly before publication. The feature illustration is an original conceptual image and does not depict the product interface.